An explicitDeny that wasn’t in my policy
The IAM policy simulator told me my web servers couldn’t upload backups. They were uploading backups just fine.
- Area
- AWS · IAM
- Project
- AWS cloud homelab
What I saw
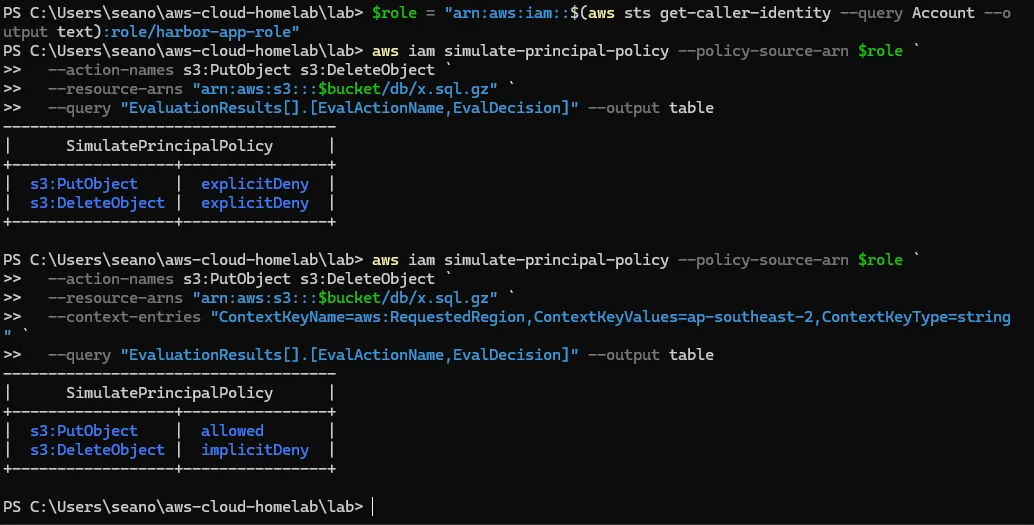
To prove the servers’ role followed least privilege, I asked the policy simulator whether it could s3:PutObject (should be allowed) and s3:DeleteObject (should be denied) on the backup bucket. Both came back explicitDeny, even though a real upload from a server had just worked.
Why it happened
My account only allows requests in one Region, ap-southeast-2. That rule is an SCP with an aws:RequestedRegion condition. A simulated request has no Region unless you give it one, so the SCP denied everything I simulated.
How I found it
The full JSON output showed that no statement in the role’s own policies matched, and that OrganizationsDecisionDetail.AllowedByOrganizations was false. An explicit deny that matches nothing in the role points above the account.
The fix
I re-ran the simulation with --context-entries setting aws:RequestedRegion to ap-southeast-2. Upload: allowed. Delete: implicitDeny. Exactly what the policy intended, and I didn’t touch the role.
Lesson: before editing a role because of an explicitDeny, check OrganizationsDecisionDetail. The deny may not be yours.